◈
No shared VPN passwords
Every developer, runner and workstation carries its own identity. There is no team password to rotate or leak.
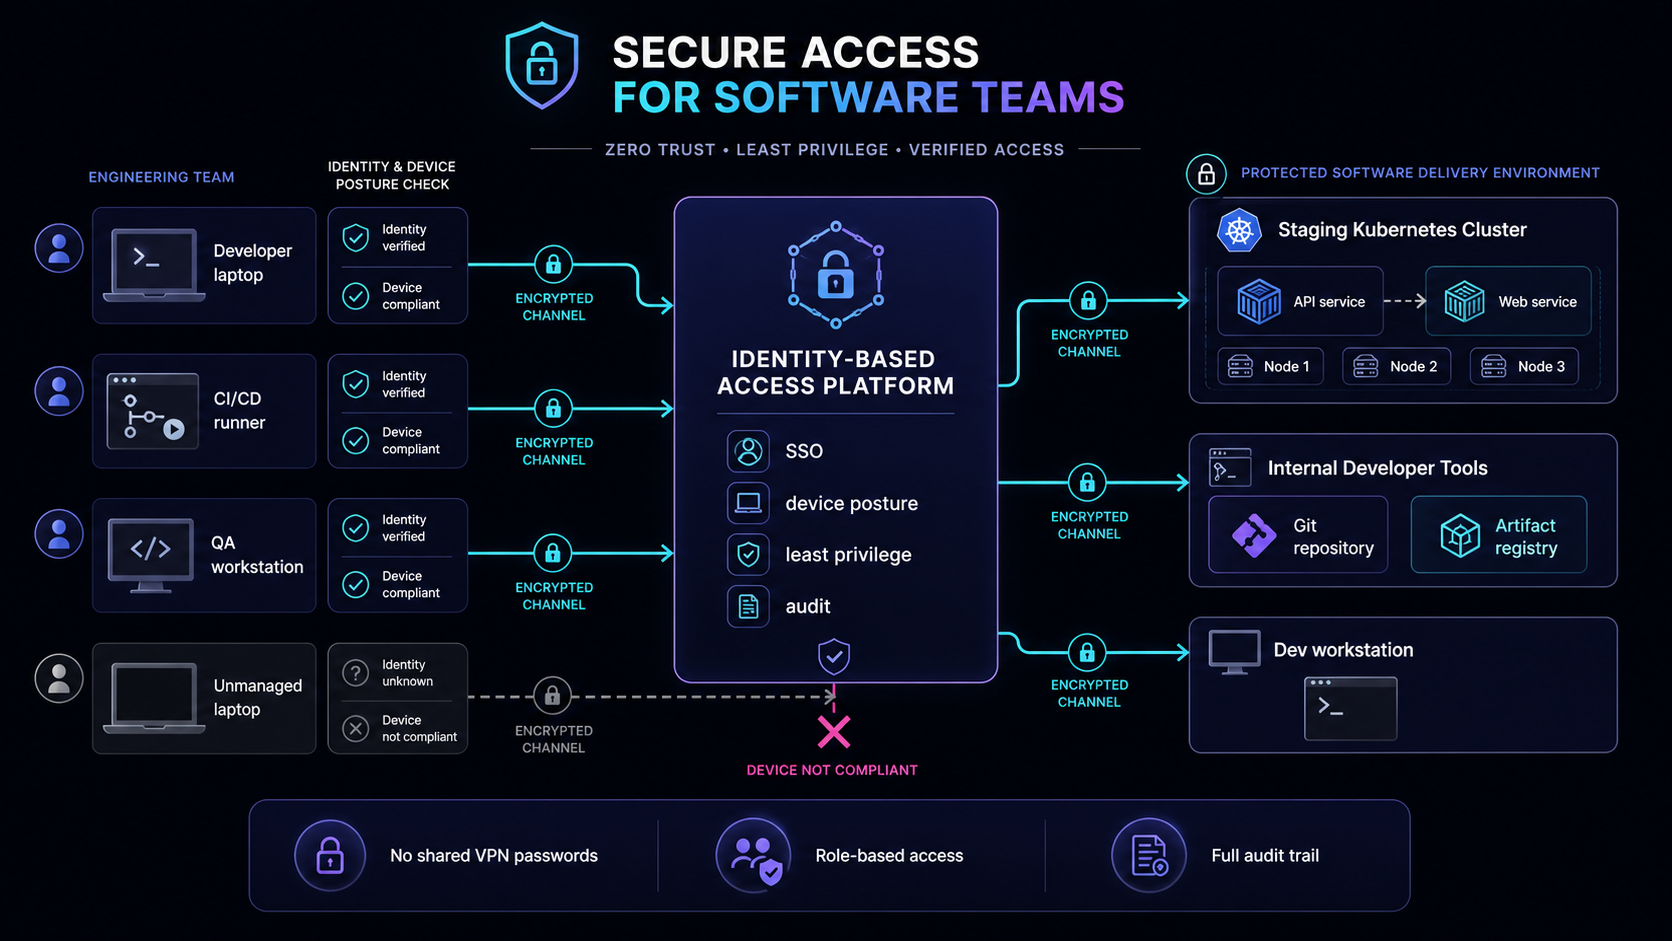
Every engineer, every CI/CD runner and every QA workstation gets its own verified identity and device-posture check, then a direct encrypted path into exactly the systems their role allows: nothing more.
Developer laptops, CI/CD runners and QA workstations each authenticate with their own identity and prove device compliance before a channel ever opens. An unmanaged or non-compliant device is blocked outright, no exception, no shared credential to leak. Everything that clears the check reaches your staging Kubernetes cluster, internal Git and artifact registry, and developer workstations over the same encrypted channel, with SSO, device posture, least privilege and a full audit trail enforced centrally.
Every developer, runner and workstation carries its own identity. There is no team password to rotate or leak.
Access to staging, internal tools and dev machines follows a developer's role, checked on every connection.
Every connection into the delivery environment is logged: who, from what device, to what system.