Every capability plugs into the same governed graph.
Control Center, Access Control, Network Routing, Reverse Proxy, DNS, Team & Identity, Activity & Audit, and Integrations: eight areas, one consistent policy model underneath all of them.
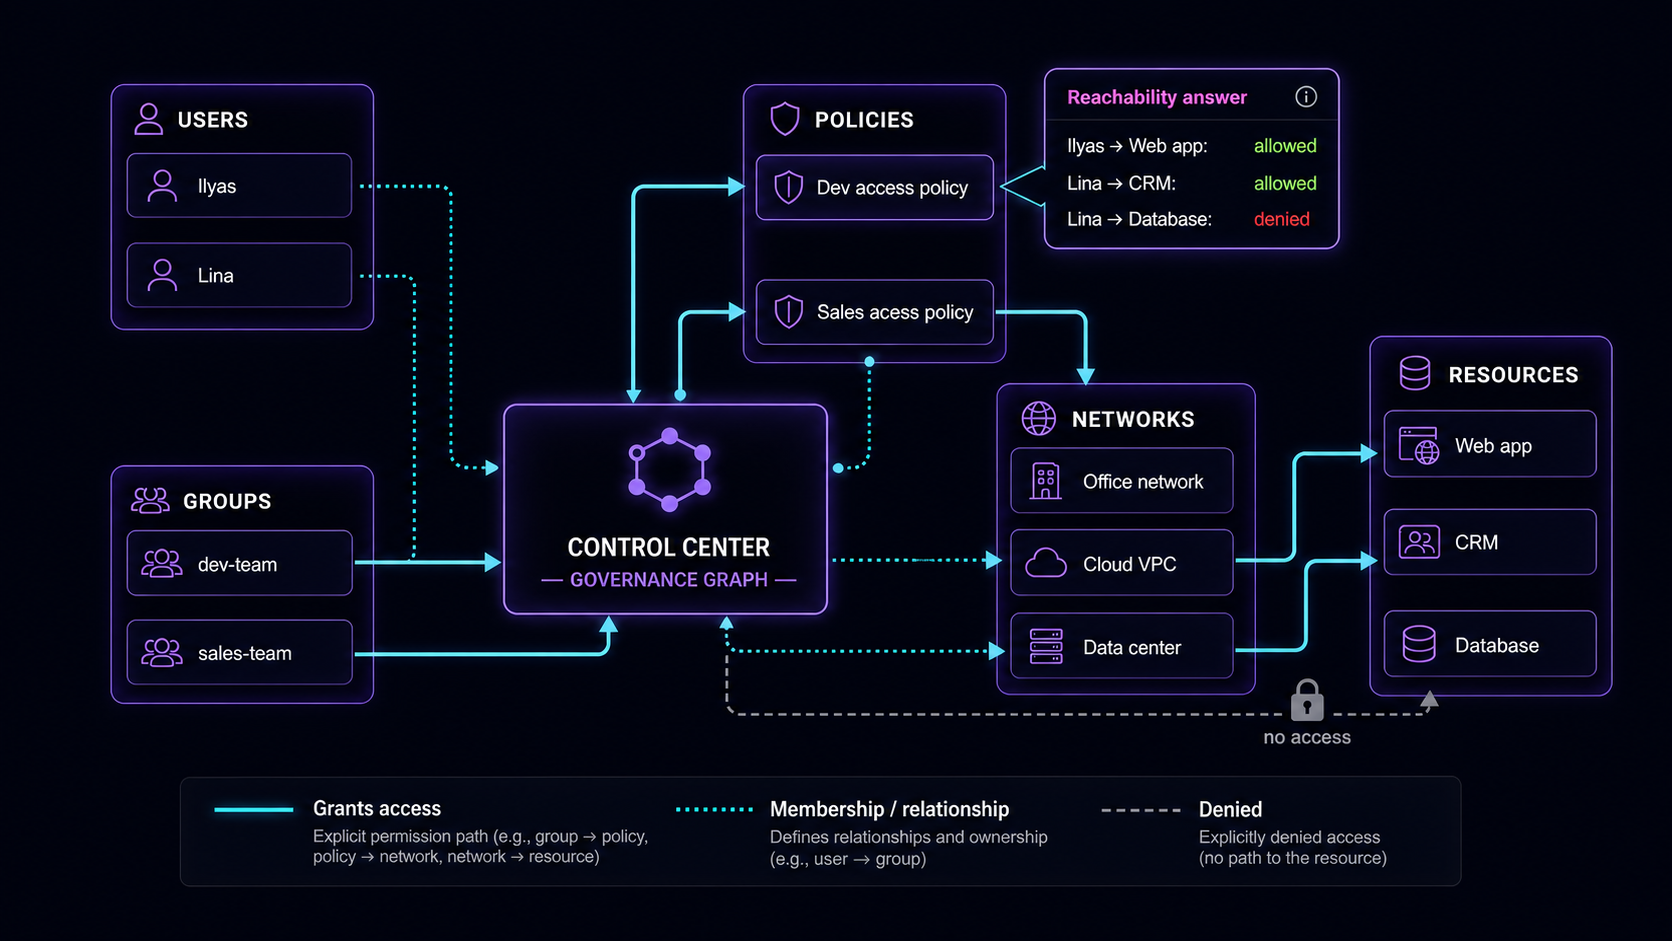
See every relationship. Govern it from one graph.
Control Center renders devices, users, groups, policies and networks as one interactive graph, so the shape of your access model is never a guess. Pivot the same graph by peer, user, group or network to see exactly what a policy actually grants, before it goes live.
- ✓Live device ↔ user ↔ group graph
- ✓Policy and network overlays
- ✓Instant reachability answers
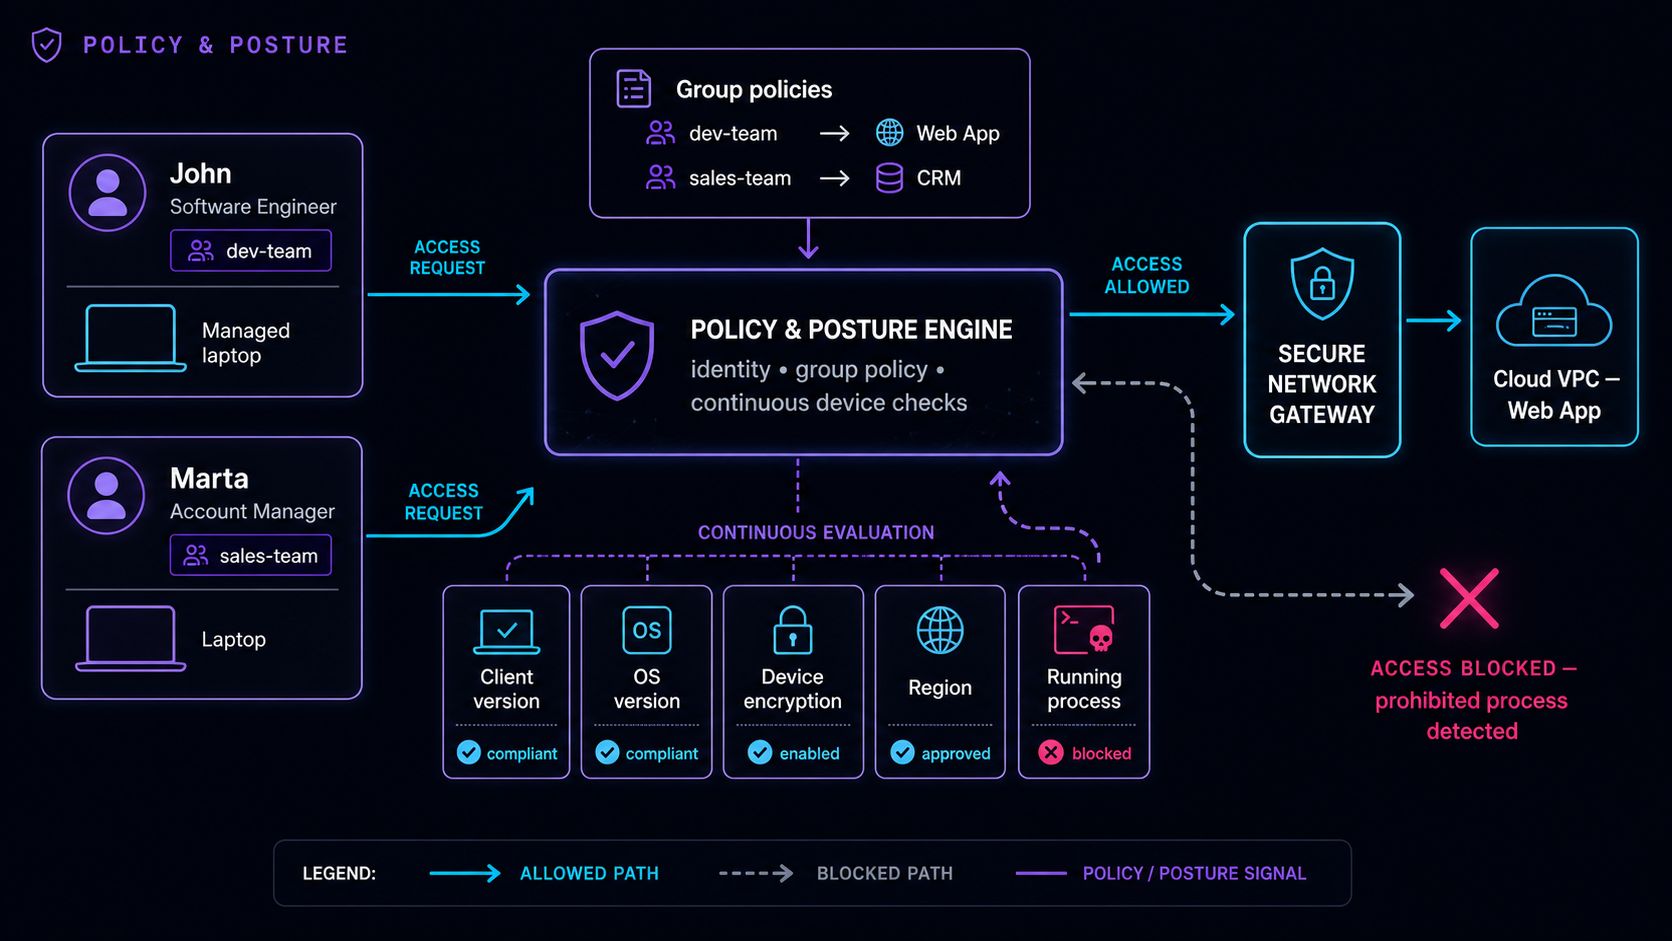
Access starts with identity. Posture decides the rest.
Define policies and groups once, then require real device posture (client version, OS, region, even a running process) before a connection is ever allowed. Posture checks evaluate continuously, not just at login.
- ✓Policy and group management
- ✓Five posture-check types
- ✓Inline policy editing, with a diff before it applies
Reach the network. Not just one machine.
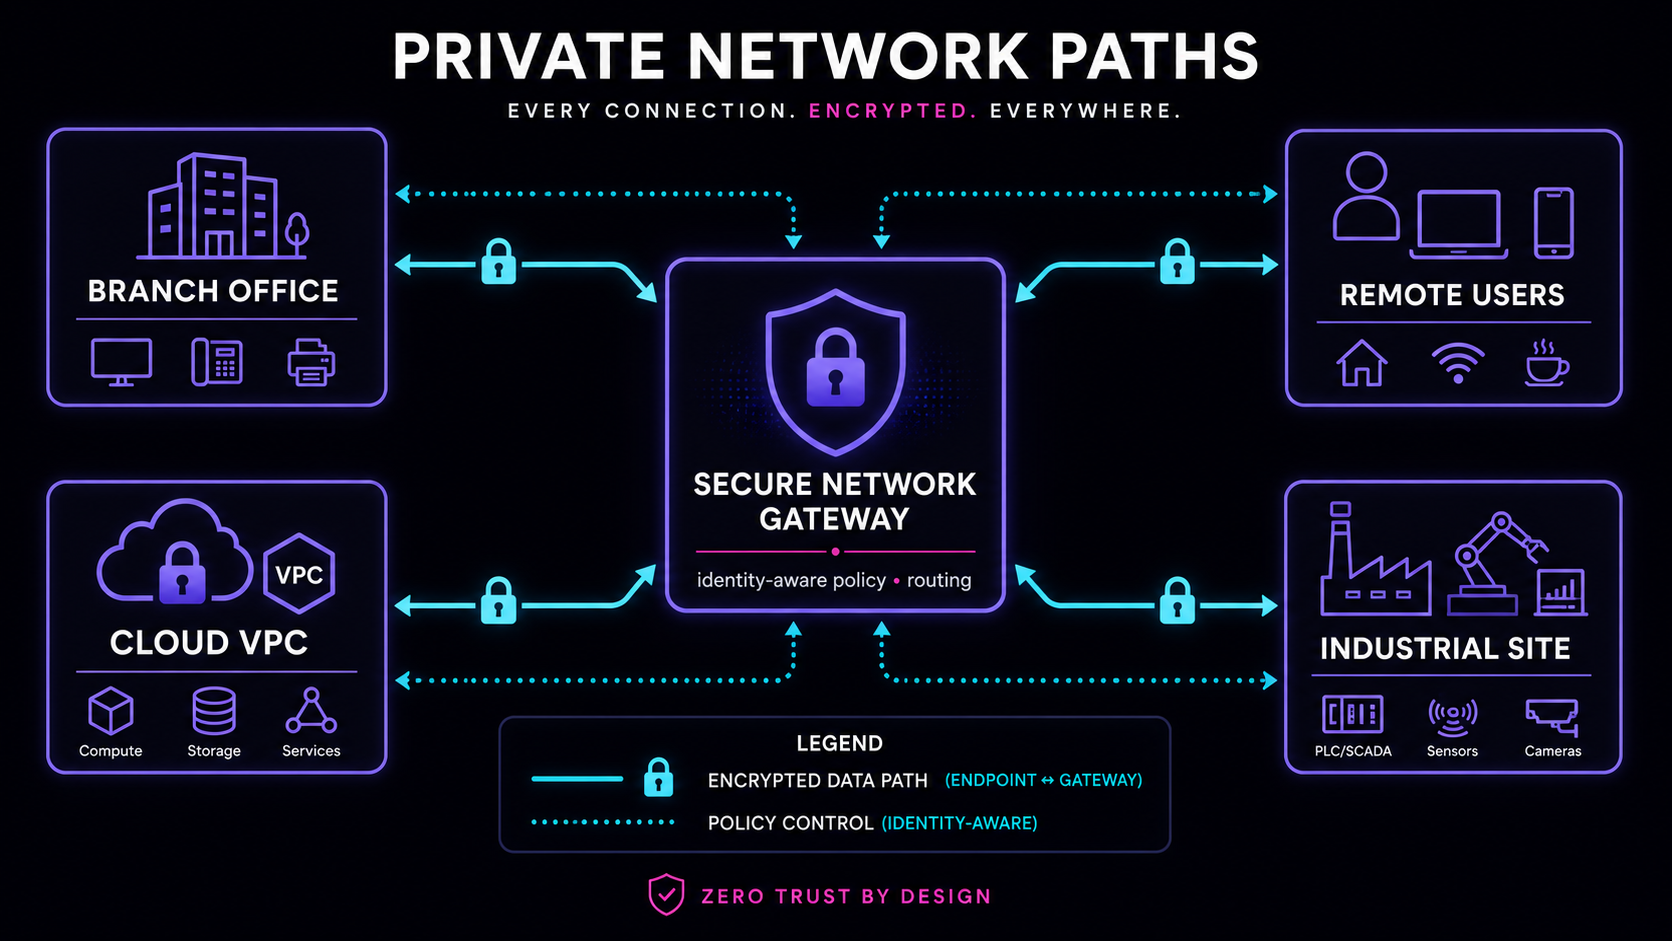
Model a Network as resources behind a router, then attach policy, so a subnet, a VPC or a site becomes one governed object instead of a list of routes.
- ✓Network → resource → router model
- ✓Address-range and domain routes
- ✓Policy applied at the network level
Publish the app. Never the network.
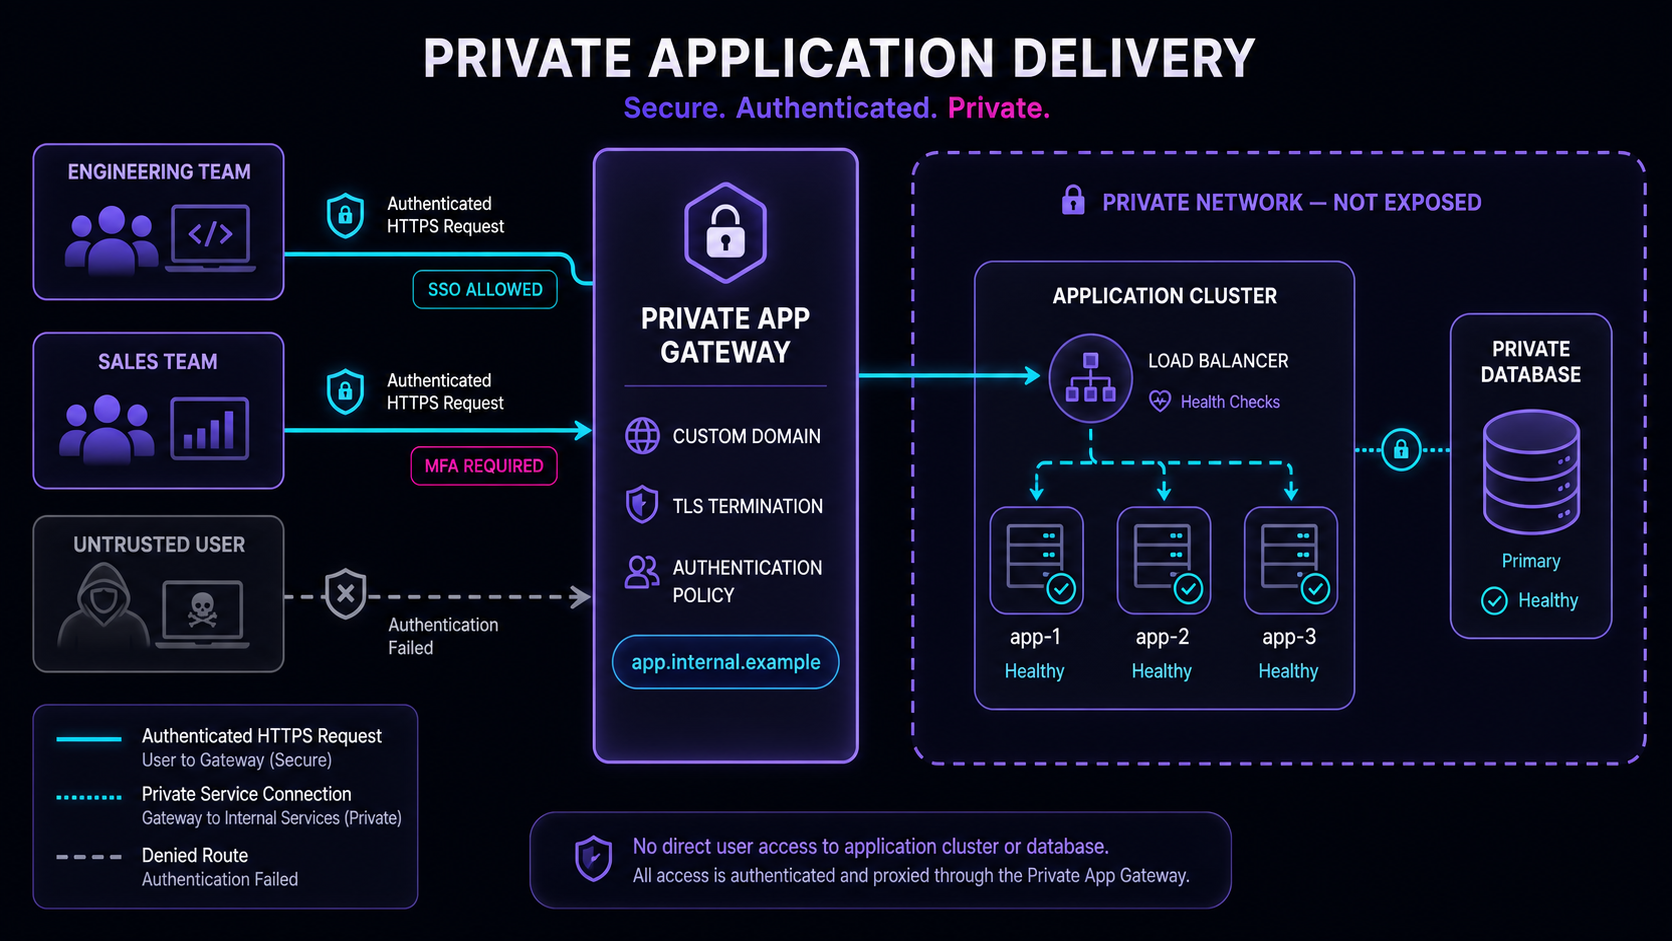
Put an internal HTTPS service behind Synapse Nexus with its own authentication layer, load-balanced cluster and custom domain, without exposing the network it runs on.
- ✓HTTPS services with custom domains
- ✓SSO, password, PIN & header authentication
- ✓Clusters for resilient delivery
Names that only your fabric can resolve.
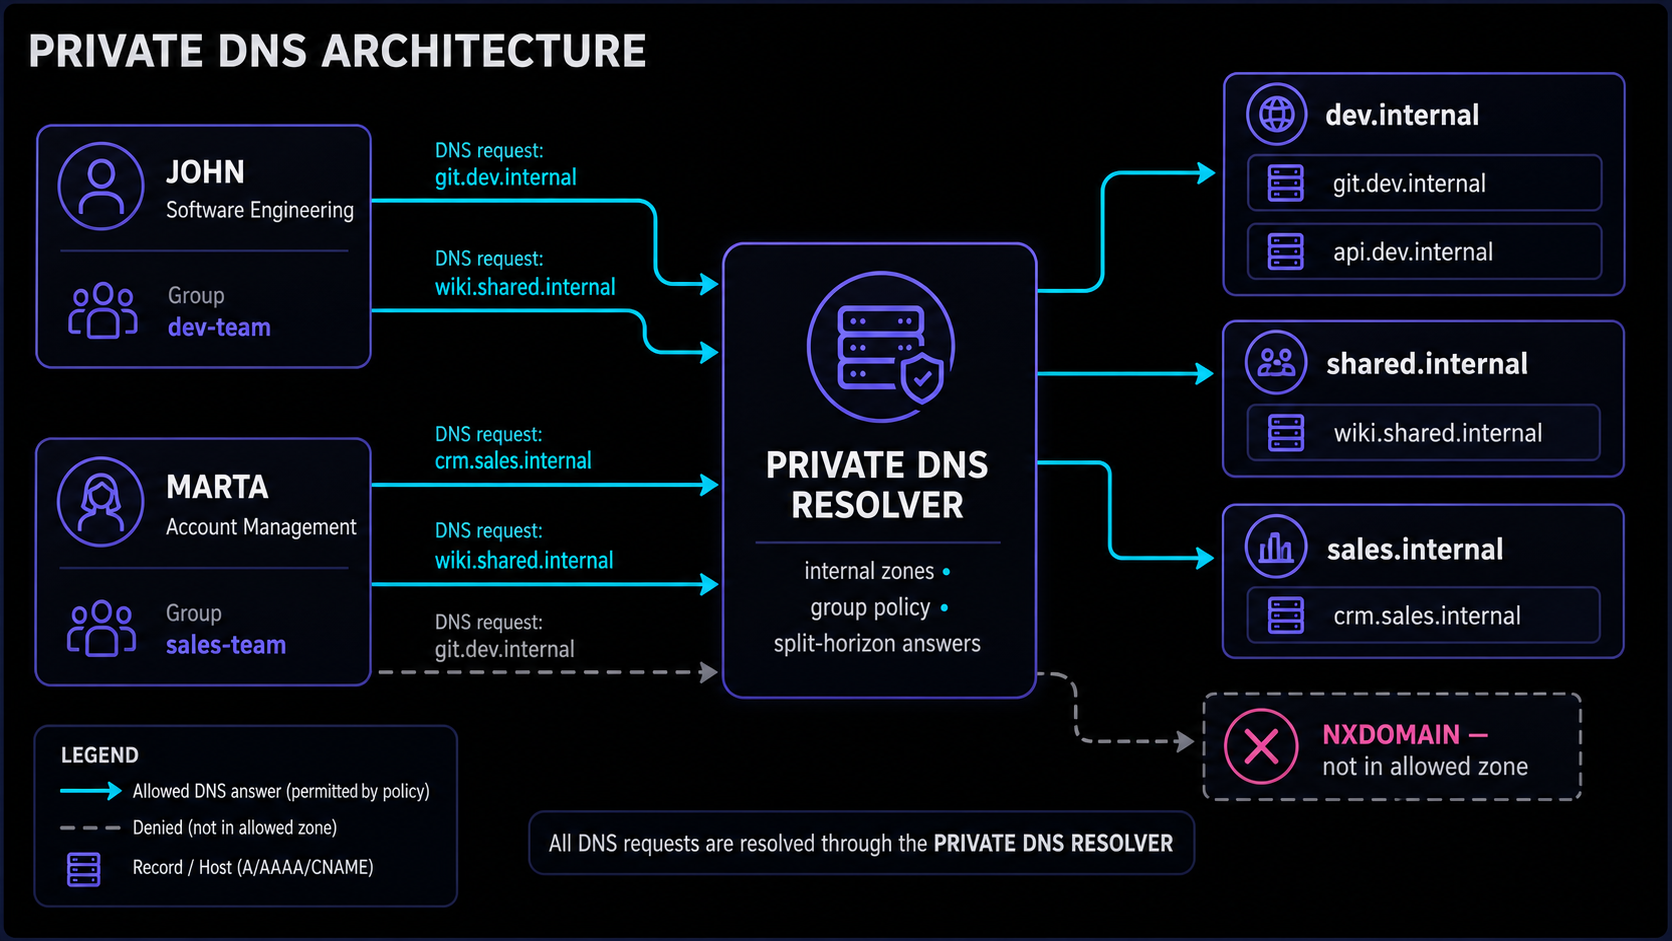
Assign nameservers and internal zones so private services get real hostnames, with group-level exceptions where you need them, so you can stop hard-coding IPs into scripts.
- ✓Custom nameserver assignment
- ✓Internal DNS zones
- ✓Group-level DNS exceptions
Every identity, the right role.
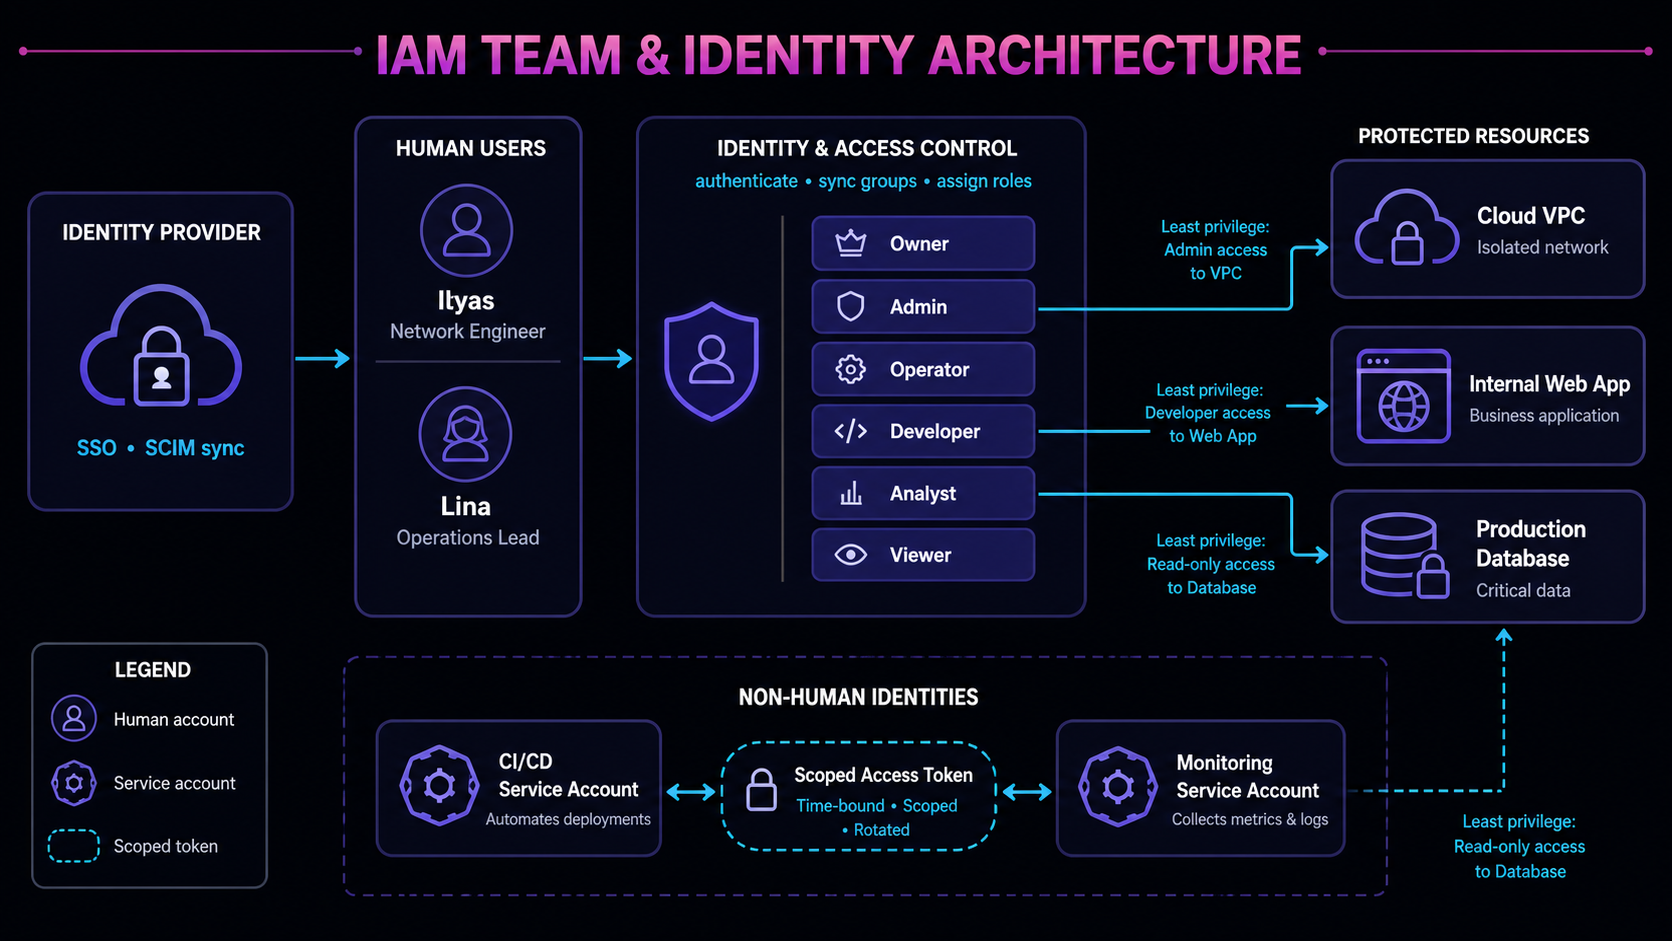
Bring people in through your existing identity provider, assign one of six roles, and issue scoped access tokens for the services that aren't people. Identity sync keeps human accounts current; service users give automation its own governed identity.
- ✓SSO & identity-provider sync
- ✓Six role levels
- ✓Service users & access tokens
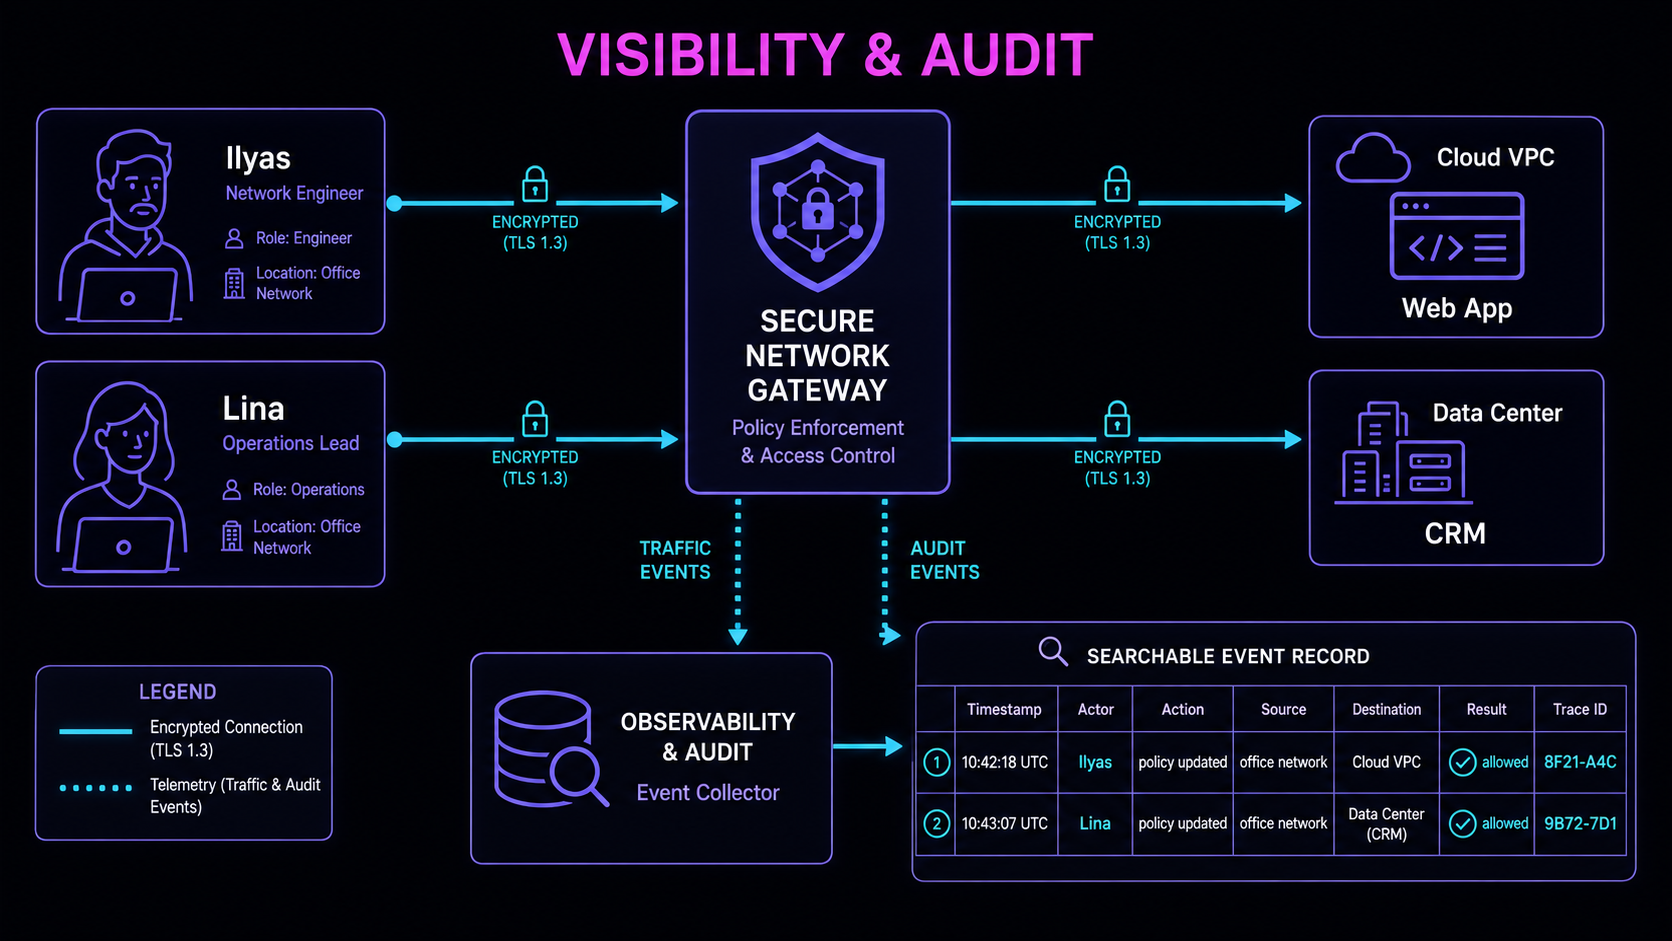
Every connection, a clear record.
Audit events capture who changed what; traffic events show which path a connection actually took; both searchable from one place, with source and destination context on demand.
- ✓Full audit event trail
- ✓Traffic event visibility
- ✓Source & destination detail on hover
Plug into the stack you already run.
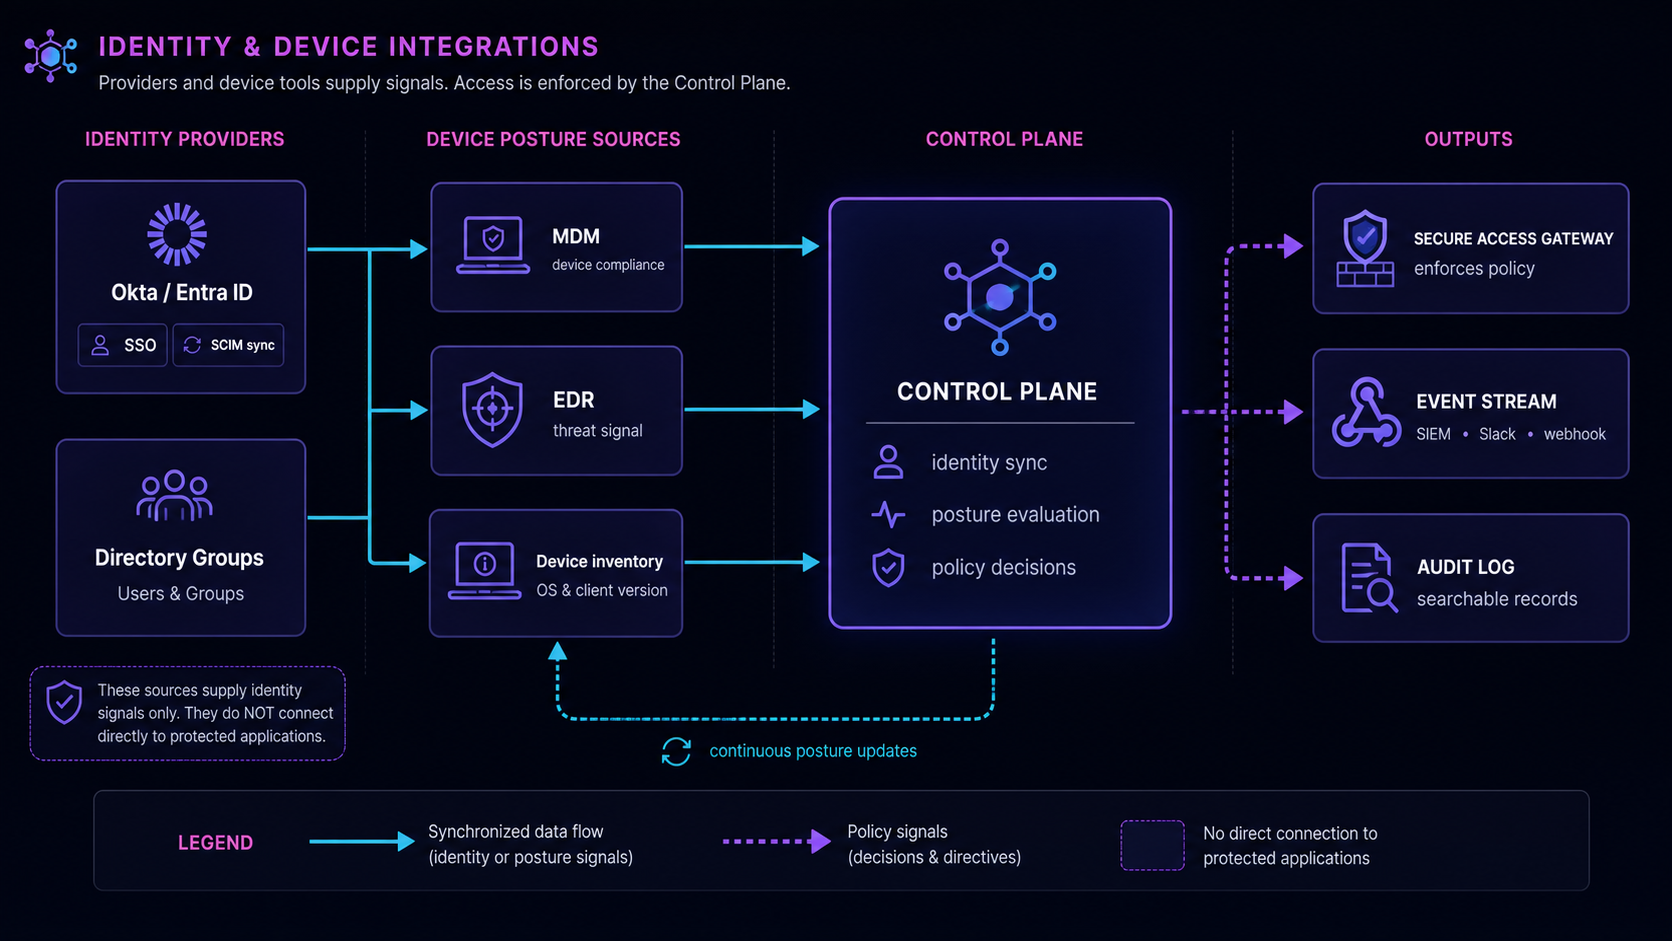
Sync identity from your provider, pull posture signals from MDM and EDR tools, and stream events to the systems your security team already watches: Intune, SentinelOne, CrowdStrike, Huntress and FleetDM.
- ✓SSO & identity-provider sync
- ✓Five MDM/EDR integrations
- ✓Event streaming: webhook & Slack