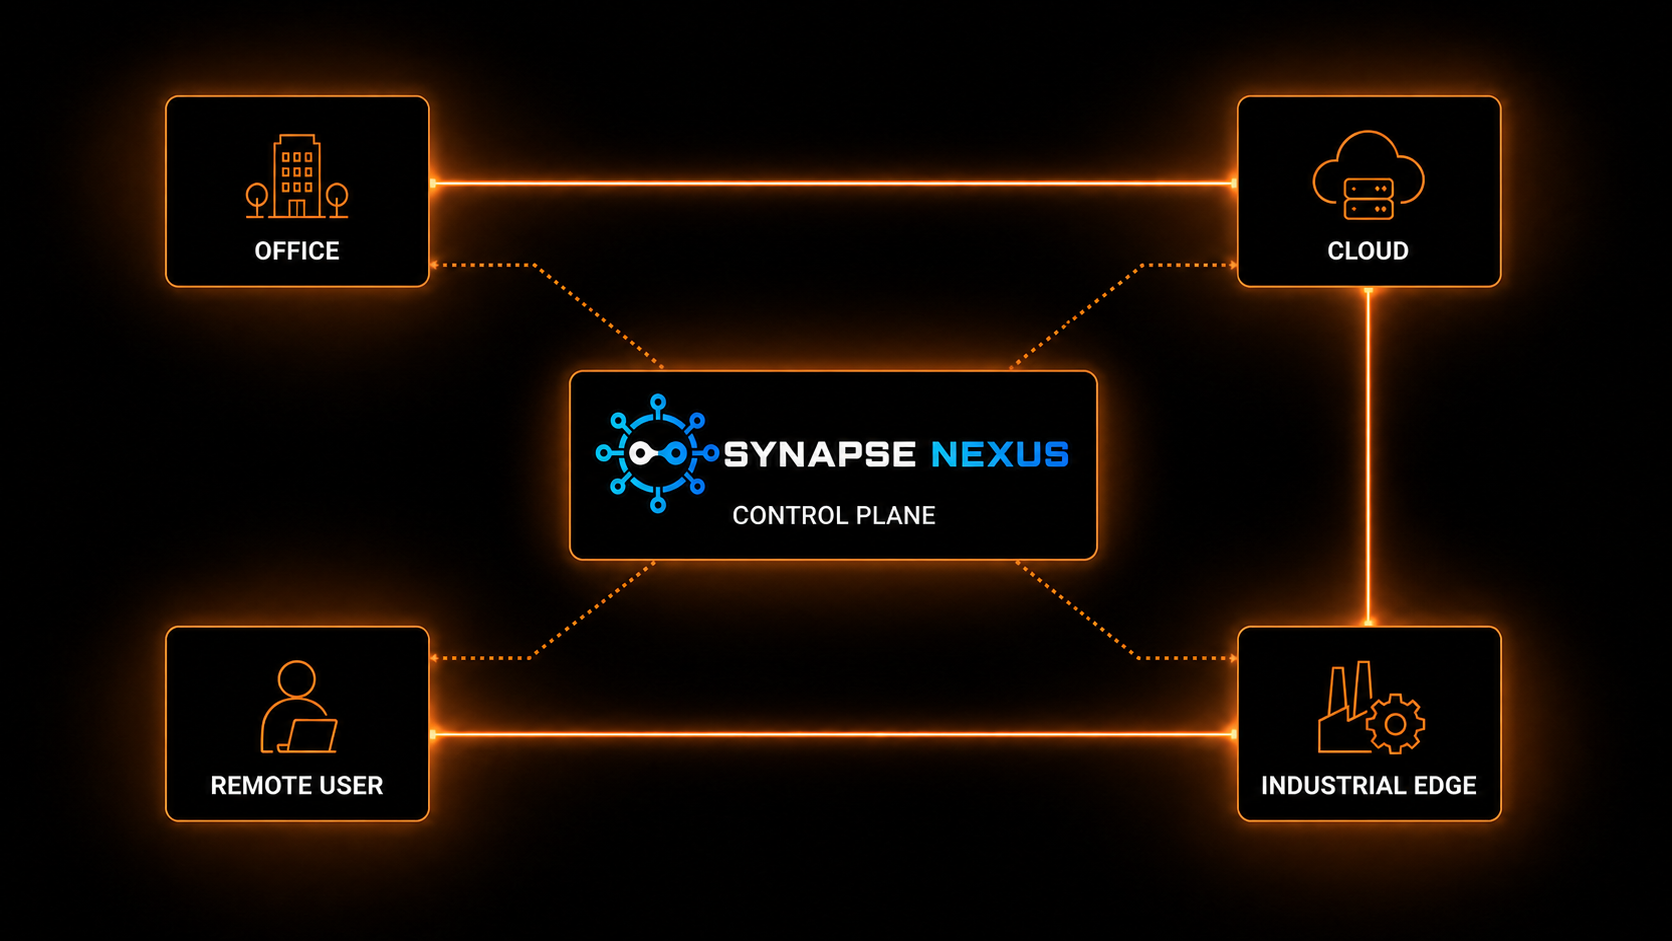
A control plane that coordinates. A mesh that carries the traffic.
Synapse Nexus's control plane is never in the data path. It hands out identities and policy; your traffic flows directly between devices, encrypted, over a WireGuard-based mesh.
The control plane coordinates. It never carries your traffic.
Every device holds its own cryptographic identity. The control plane's only job is to tell two devices that are allowed to talk to each other how to find one another; the actual connection is negotiated directly between them and encrypted end to end.
- ✓A stable, private identity per device on enrollment
- ✓Direct, encrypted peer-to-peer paths
- ✓The control plane coordinates who's allowed to reach whom, nothing more
Built on a WireGuard-based mesh.
Every connection is a real WireGuard tunnel: modern, auditable cryptography, not a proprietary protocol. Clients that already speak WireGuard are drop-in compatible; there's no custom handshake to trust blindly.
- ✓Modern, widely-audited cryptography
- ✓Drop-in compatible clients
- ✓No custom, closed handshake to trust
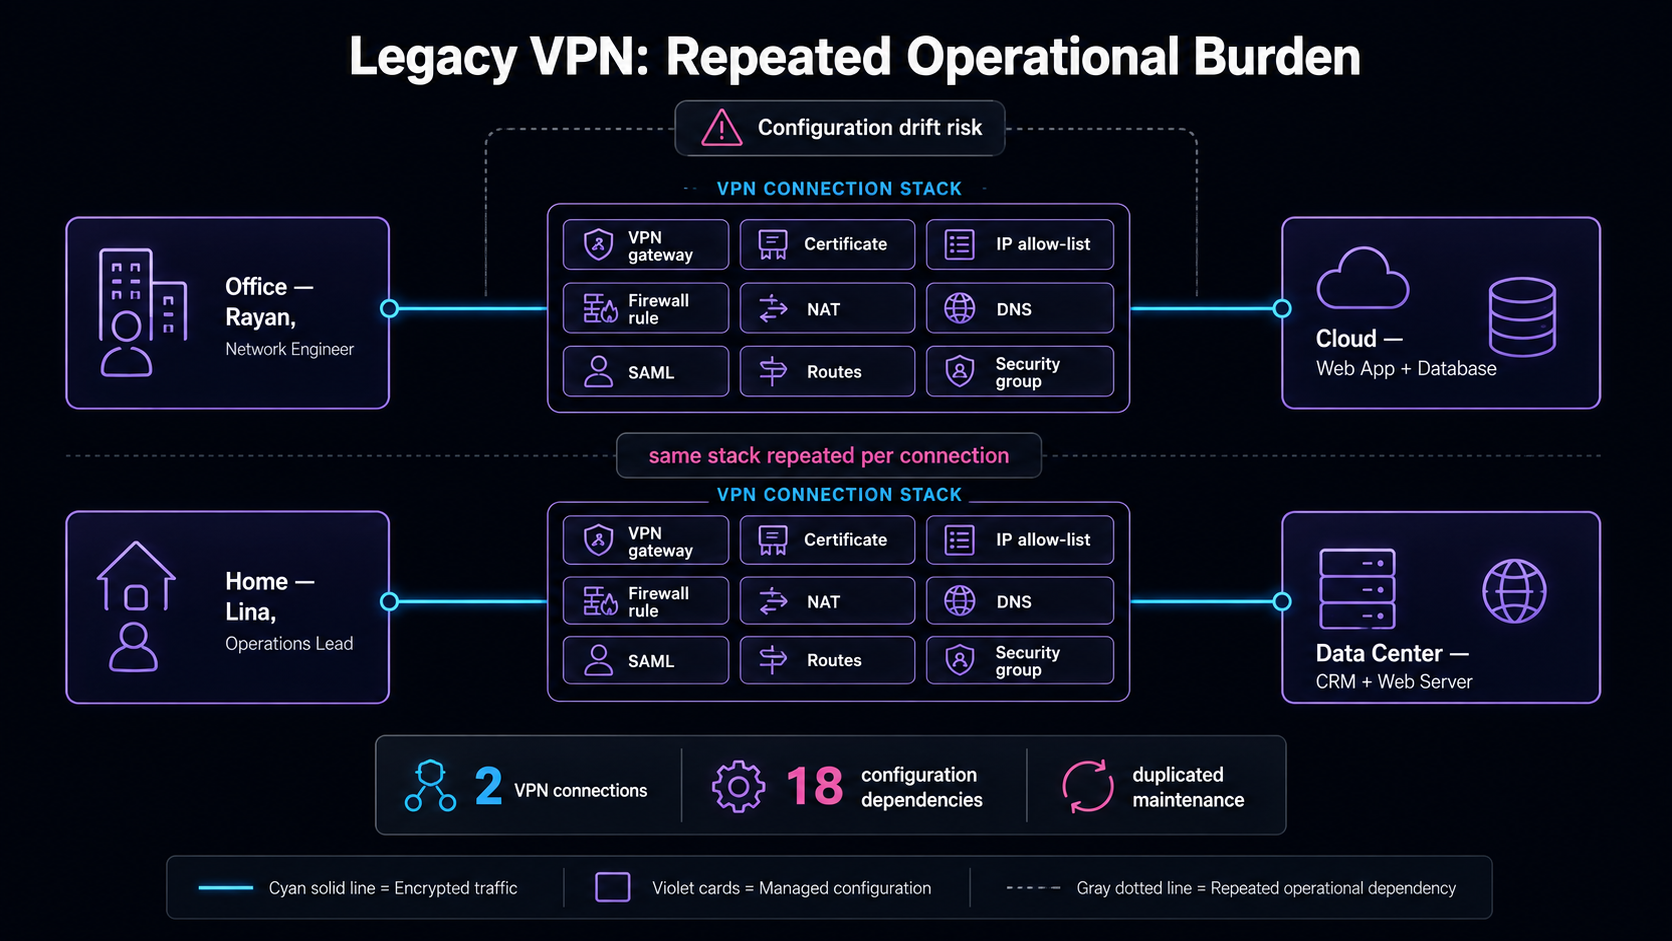
Every VPN connection repeats the same operational burden.
Gateways, certificates, IP ranges, firewall rules, NAT, DNS, SAML, all multiplied across every site and every connection. Synapse Nexus replaces that stack with one governed graph.
Network Routing and Reverse Proxy, governed from the same graph.
Every path, office, cloud, remote user or industrial edge, resolves through the same policy layer before a connection is ever made.
Office
Site-to-site connectivity without a dedicated VPN concentrator.
Cloud
Reach private VPCs and services through Network Routing's resource model.
Remote user
Identity and posture decide access, not which network someone is on.
Industrial edge
DNS and OT devices reachable under the same governed policy.