◇
Private VPC reachability
All sensitive services stay private within your VPC, across AWS, Azure or GCP.
Reach private VPCs and services through Network Routing's resource model. Web, data and operations subnets stay fully private, AWS, Azure or GCP, and every request is evaluated before it ever reaches a service.
An authorized developer on a trusted device connects over an identity-based encrypted mTLS channel; an approved external browser goes through a reverse-proxy HTTPS front door. Both paths hit the identity policy engine first, which checks who you are, your device's health and trust, and exactly what you're allowed to reach, before anything is allowed through. Inside the VPC, the web/API subnet's internal load balancer and containerized workloads stay private behind that reverse proxy; the data subnet's database is never exposed to the public internet and is encrypted at rest; the operations subnet's monitoring and log collection stay private and centrally encrypted. An unauthorized identity or an untrusted device is denied outright.
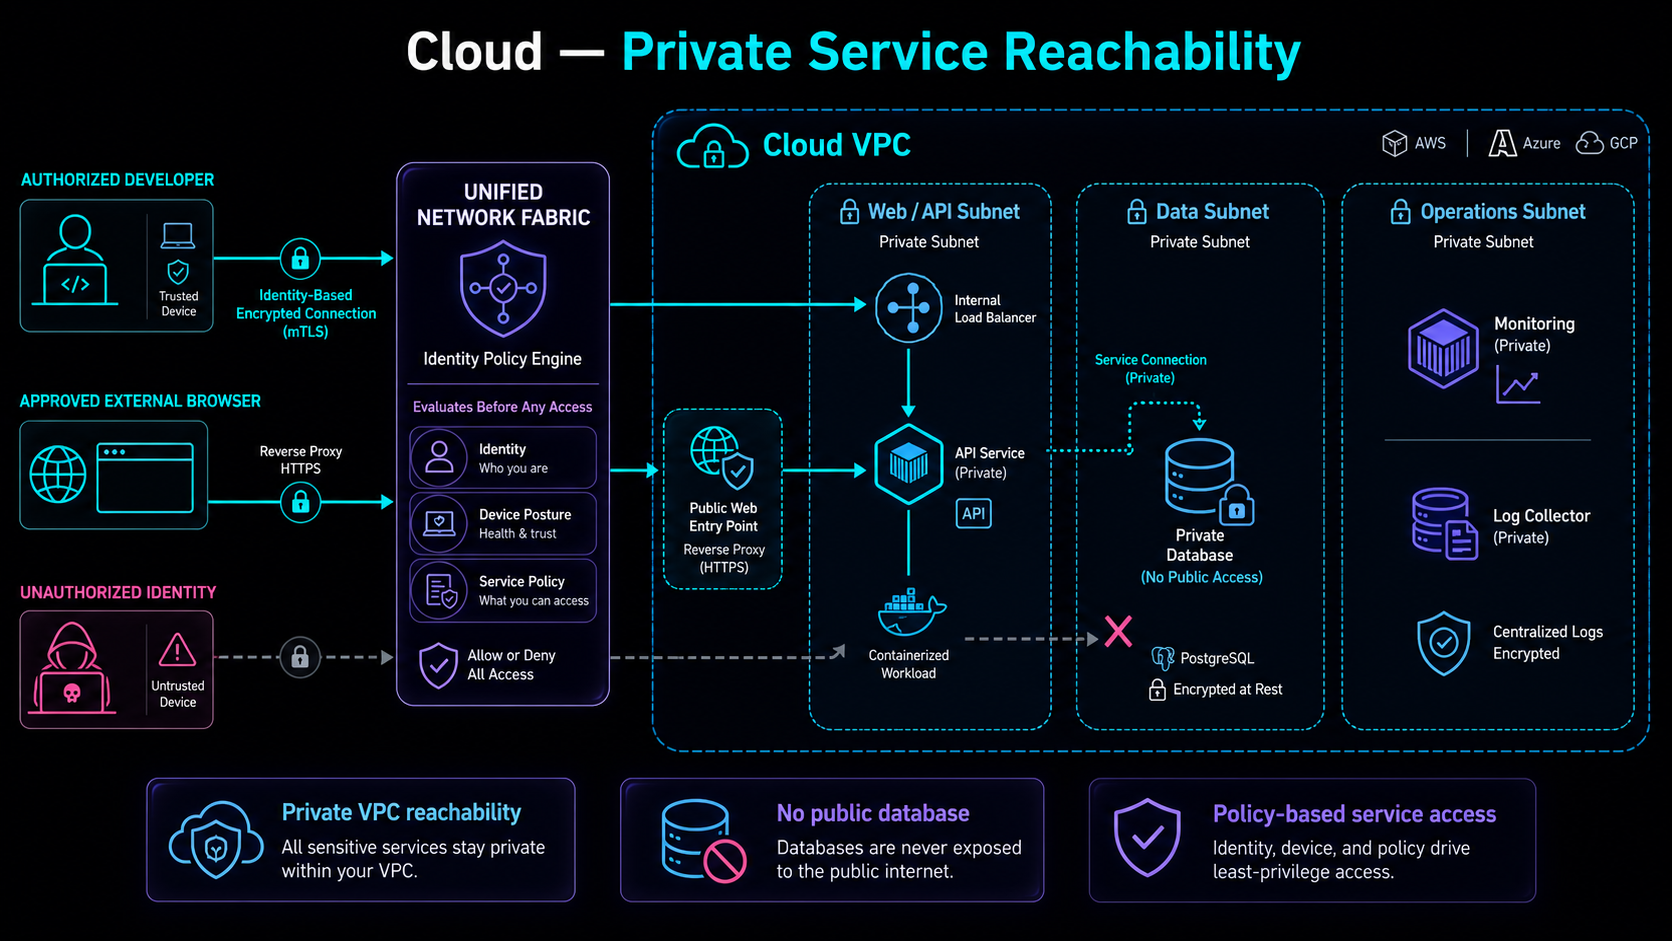
All sensitive services stay private within your VPC, across AWS, Azure or GCP.
Databases are never exposed to the public internet, and stay encrypted at rest.
Identity, device and policy together drive least-privilege access to every service.