⌘
Safe OT segmentation
Micro-segmentation and protocol-aware controls protect critical industrial assets.
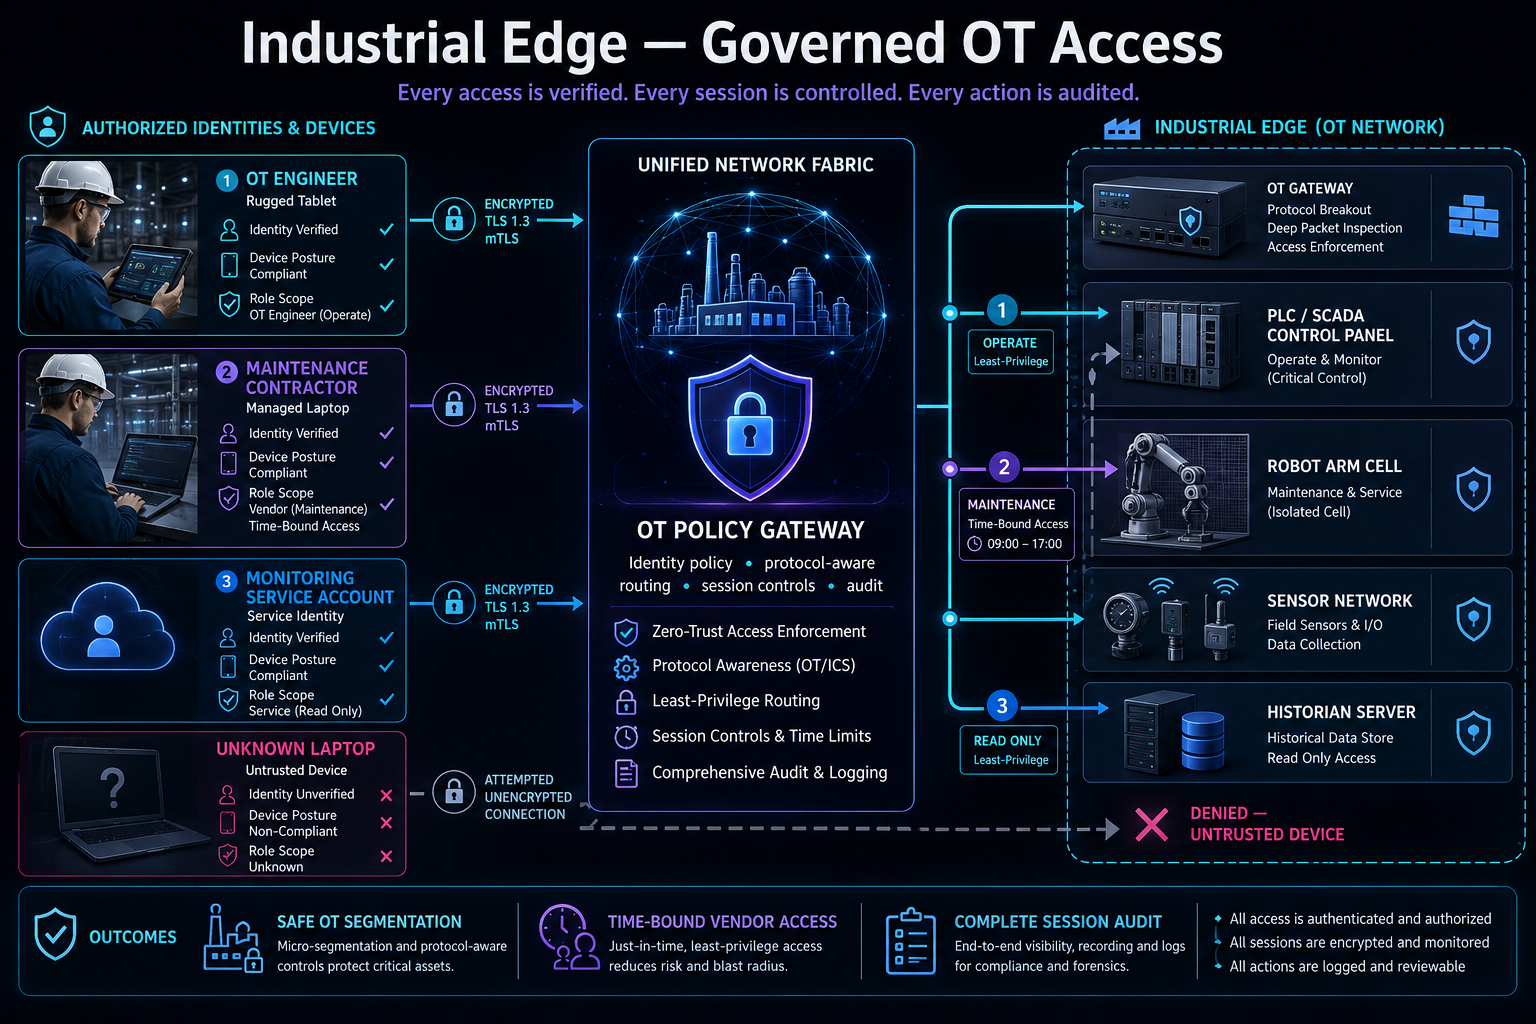
DNS and OT devices are reachable under the same governed policy as everything else. An OT policy gateway enforces identity, protocol-aware routing, session limits and full audit, down to a single PLC or robot arm cell.
An OT engineer on a rugged tablet, a maintenance contractor on a managed laptop, or a monitoring service account each connect over an encrypted TLS 1.3 mTLS channel with their identity verified, device posture confirmed and role scope checked, operate, time-bound maintenance, or read-only. The OT policy gateway then applies identity policy and protocol-aware routing (OT/ICS aware, not just IP), session controls and time limits, and comprehensive audit logging before routing that specific role into exactly its slice of the industrial edge: an OT gateway doing protocol breakout and deep packet inspection, a PLC/SCADA control panel, an isolated robot-arm cell, a field sensor network, or a read-only historian server. An unknown or untrusted device attempting an unencrypted connection is denied outright.
Micro-segmentation and protocol-aware controls protect critical industrial assets.
Just-in-time, least-privilege access for contractors reduces risk and blast radius.
End-to-end visibility, recording and logs for every session, for compliance and forensics.