◈
No dedicated VPN concentrator
Lower cost and a simplified architecture: one managed branch router replaces a per-site VPN gateway.
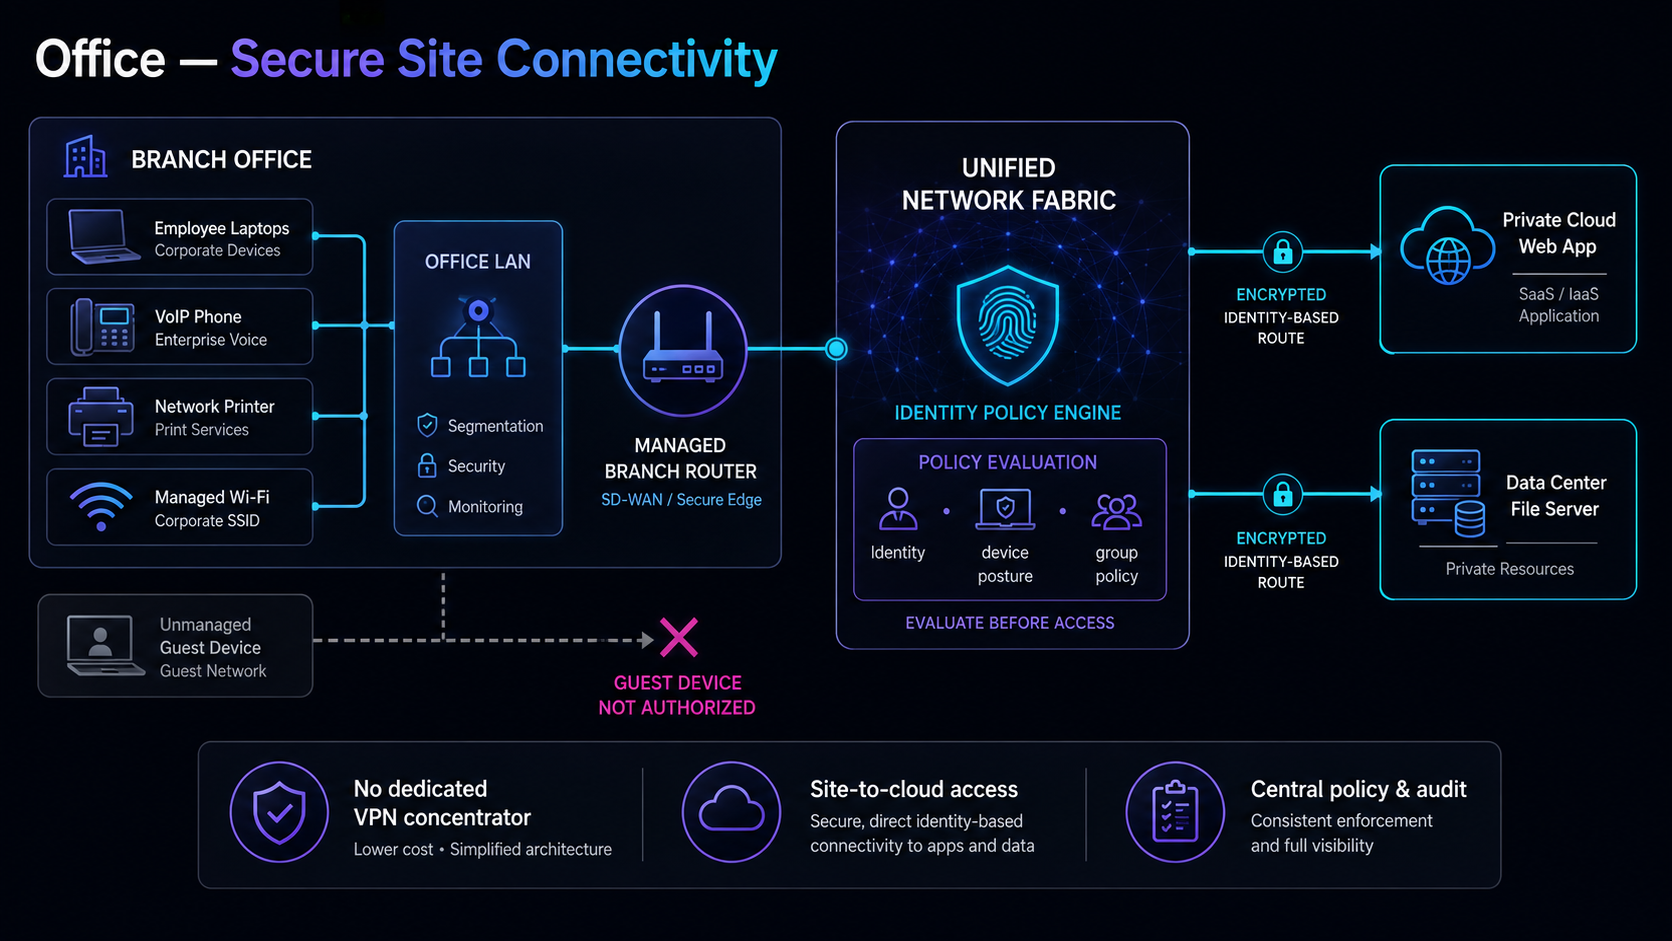
Every device on a branch office LAN, laptops, VoIP phones, printers, managed Wi-Fi, reaches private cloud apps and the data center through one identity policy engine, not a gateway per site.
The office LAN, segmented, secured and monitored, connects out through a single managed branch router (SD-WAN / secure edge) into the unified network fabric. Before any traffic is allowed, the identity policy engine evaluates identity, device posture and group policy together, then opens an encrypted, identity-based route to exactly the private cloud web app or data center file server that connection is allowed to reach. An unmanaged guest device on the same office Wi-Fi never gets a route at all.
Lower cost and a simplified architecture: one managed branch router replaces a per-site VPN gateway.
Secure, direct, identity-based connectivity from the branch office straight to private apps and data.
Consistent enforcement and full visibility across every office, from one policy engine.