✦
No location-based trust
Access is granted based on verified identity, device posture and context, not location.
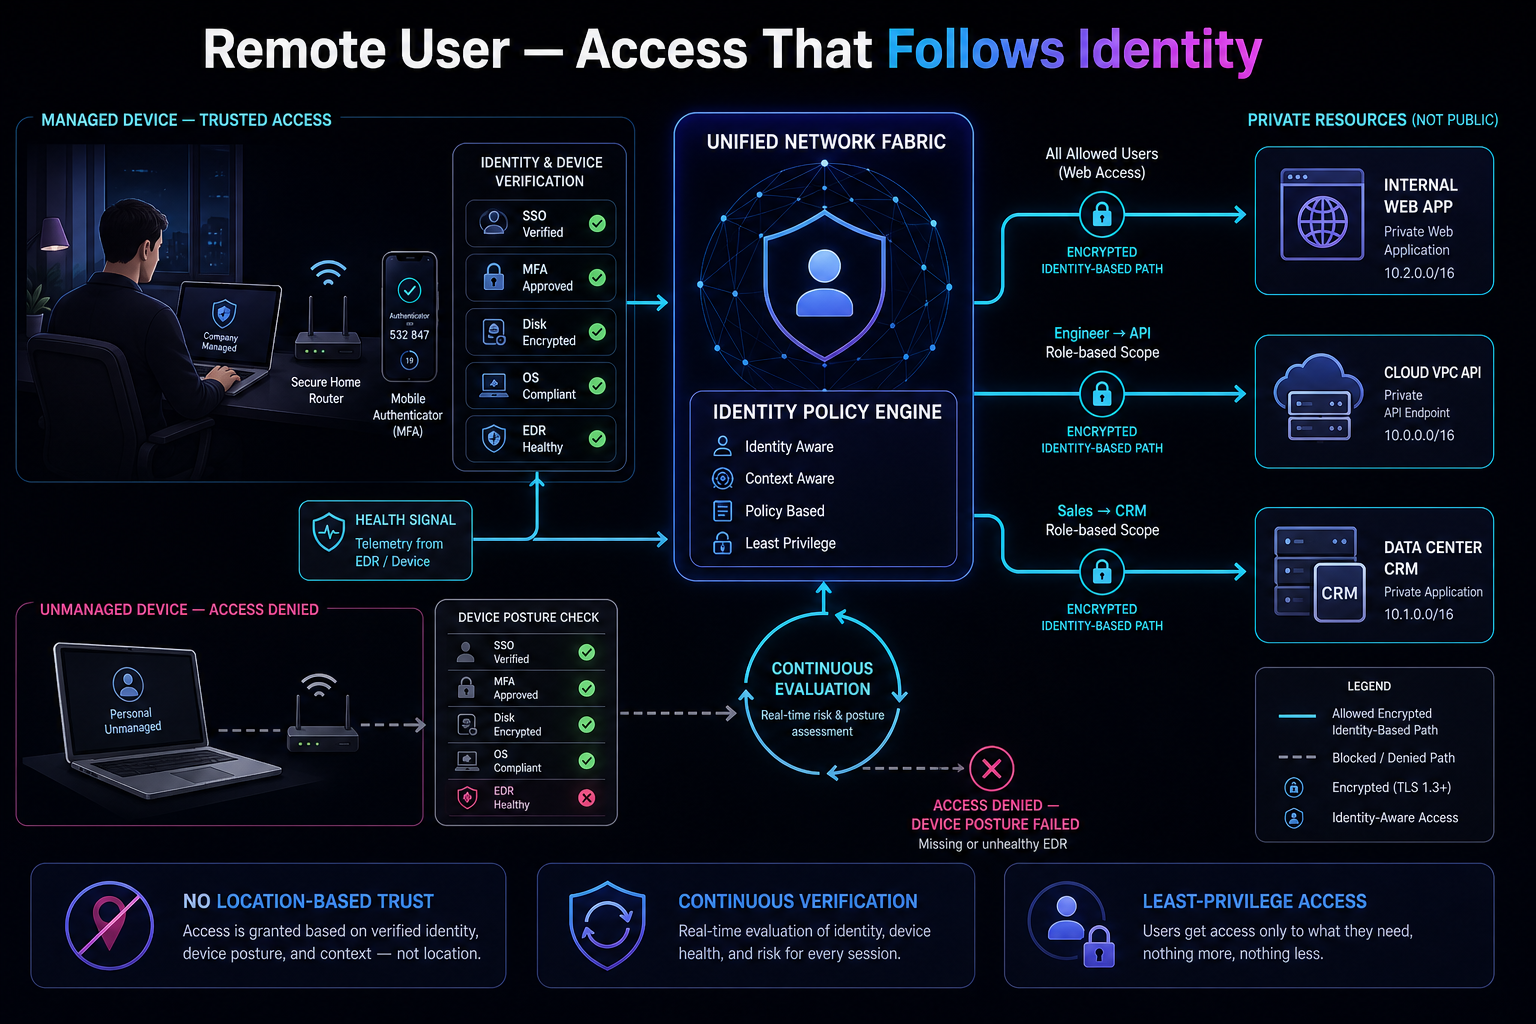
Identity and posture decide access, not which network someone is on. A managed, compliant device gets a role-scoped path to exactly the apps it needs; an unmanaged one is denied before it ever reaches the fabric.
A managed device signs in through SSO and MFA, proves disk encryption, OS compliance and a healthy EDR agent, then sends that health signal into the identity policy engine, which is identity-aware, context-aware, policy-based and enforces least privilege on every route it opens. From there, role-scoped, encrypted paths open exactly where that identity is allowed: all users to the internal web app, an engineer to the cloud VPC API, sales to the data-center CRM, nothing more. The engine doesn't stop checking at login: a continuous-evaluation loop keeps re-assessing risk and posture in real time, so a device that later fails its posture check (say, EDR goes unhealthy) loses access immediately, wherever it's connecting from.
Access is granted based on verified identity, device posture and context, not location.
Real-time evaluation of identity, device health and risk for every session, not just at login.
Users get access only to what they need, nothing more, nothing less.